
ABDM Compliance for Hospitals in 2026 ABHA, Health Record Sharing and AB-PMJAY Requirements
Now that the time is coming for India to digitise all of its healthcare services, the Ayushman Bharat Digital Mission has become a critical component in any hospital’s strategic planning. ABDM compliance is a must for hospitals seeking to optimise their processes, as well as utilise India’s budding health insurance system to its fullest.
In this blog, we will explore what steps hospital admin and IT directors need to take in order to become ABDM compliant by 2026.
Health Records Sharing and AB-PMJAY Compliance Requirements
The creation of an Ayushman Bharat Health Account (ABHA) needs to be integrated into the OPD and Inpatient admission processes. This can be done by creating a new ABHA ID at the registration desk for easier processing.
Alternatively, the hospital can implement Aadhaar or mobile number verification at the front desk for faster patient registration. The existing medical records of a patient should be uploaded onto their new ABHA health ID so that it becomes easier for physicians to browse through a patient’s medical history even if they switch between different facilities.
Integration of Health Records Sharing and Interoperability
It is no longer possible for the hospital to operate in isolation, as the new regulations push towards greater digitalisation of health records across facilities.
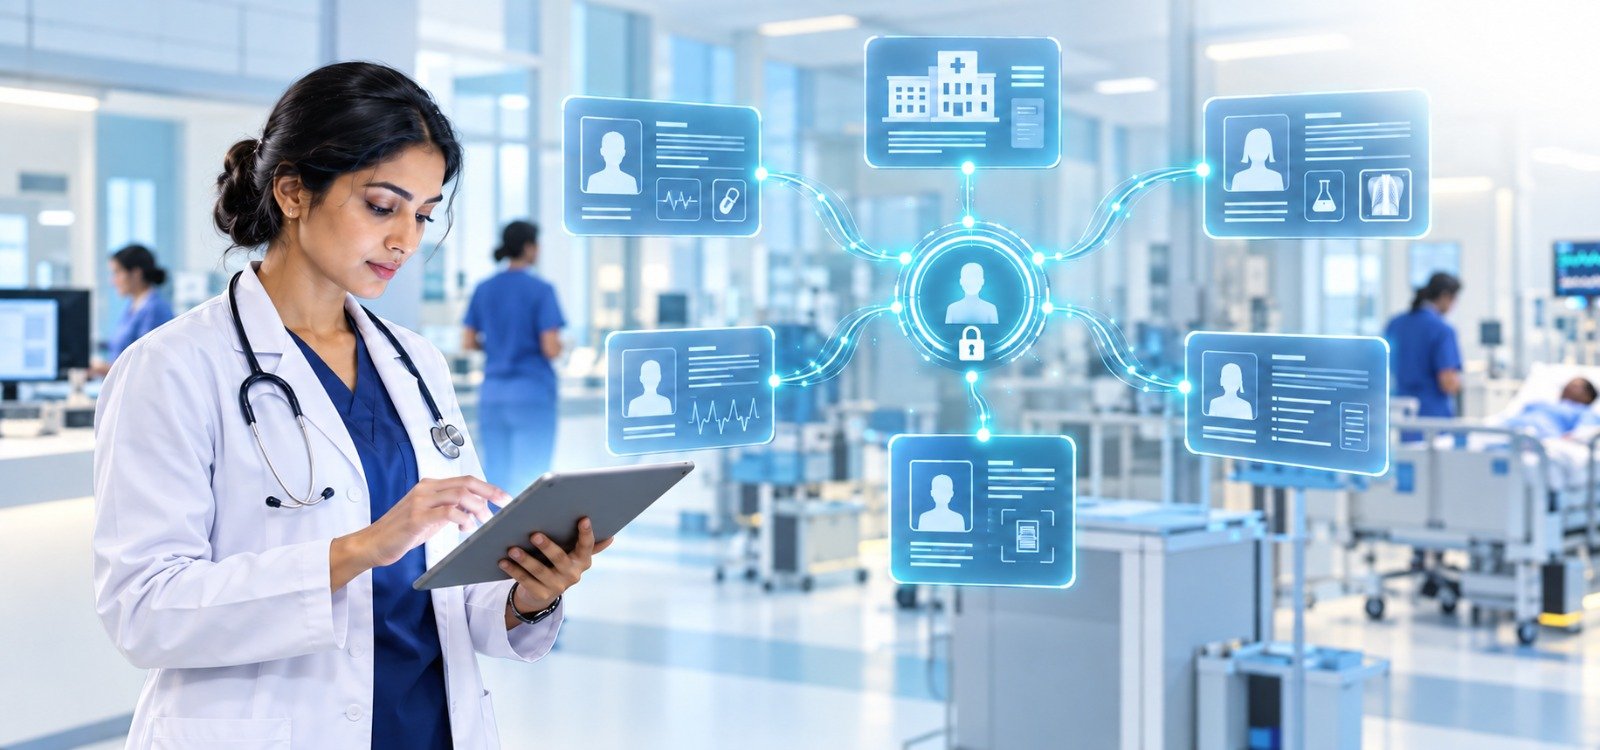
Hospital directors need to ensure that the organisation’s health-tech stack is capable of interacting with the Ayushman Bharat Health Information Exchange and Consent Manager (ABHIM/HIE-CM). Notably, the organisation will have to register on the Health Facility Registry (HFR) and Healthcare Professionals Registry (HPR). The hospital’s EHR system will need to be compatible with the Fast Healthcare Interoperability Resources (FHIR) standard in order to share medical records, notes, and prescriptions in the stipulated format.
Doctors and other medical staff can only share patient data after obtaining the necessary consents. It is recommended that the hospital invest in a system which allows patients to give their consent online.
Adherence to AB-PMJAY Guidelines and Utilisation of its Benefits
Since many hospitals will be empanelled with the Ayushman Bharat Pradhan Mantri Jan Arogya Yojana (AB-PMJAY), it is important for hospital IT directors to ensure that the facility’s processes are compatible with the guidelines set by the AB-PMJAY transaction management system (TMS).
The most important step here is to ensure seamless connectivity and data exchange between the local hospital management system and the new 2026 AB-PMJAY TMS guidelines. This will allow the hospital to utilise the benefits of paperless, faster pre-authorisation and reimbursement processes. If the hospital plans to submit insurance claims through an online application, it will have to implement biometrics and audit trails for all treatments covered under the scheme as a method of fraud detection and prevention.
Challenges with Implementing These Guidelines and How to Overcome Them
There are a number of difficulties that a hospital can face while trying to digitise its processes and comply with the new ABDM regulations. The hospital’s IT staff may run into problems trying to adapt their existing Hospital Information System (HIS) to the needs of the new ABDM-compliant healthcare ecosystem.
The main challenge here is the sheer complexity of the system, as well as integrating it with existing systems like the hospital’s accounting and billing software.
It is recommended that the hospital invest in middleware applications which can convert data into FHIR format for seamless sharing between different hospital departments. Directors can also conduct extensive training for the staff in order to prepare them for guiding patients and answering their questions about ABDM, ABHA and the consent process. An experienced team of doctors, nurses, and accountants can make all the difference during the initial stages of implementing these new processes.
Finally, it is also important to have dedicated cybersecurity experts within the hospital administration in order to ensure that the cybersecurity policies are updated in order to counter threats to the connected network, especially after the data is shared between different nodes in the network. The introduction of new data storage facilities, applications, and network connections can create blind spots in the cybersecurity system which can be exploited by cybercriminals. Having a dedicated cybersecurity committee within the hospital can help in mitigating these risks.
Conclusion
By digitising its processes and investing in new technology solutions for a seamless data exchange with other facilities and insurance providers, a hospital can ensure that it is future-proof and can provide better patient care. Preparing for ABDM compliance can offer substantial benefits to hospitals, including a reduction in paperwork and faster insurance claims settlement.

Author